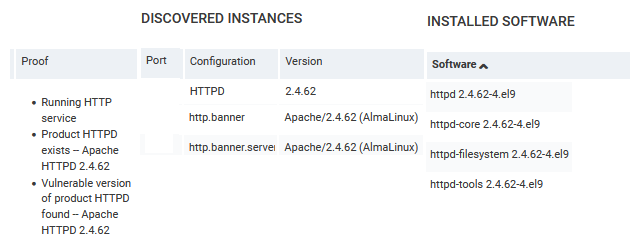
Within AlmaLinux 9.6 our vulnerability tool flagged the HTTPD 2.4.62 service as vulnerable for several CVE’s like for CVE-2024-42516, CVE-2025-53020, CVE-2025-49630, and CVE-2025-49812.
But it did not flag the httpd 2.4.62-4.el9 application itself.
From what I can see on the website, there doesn’t seem to be any vulnerability, it’s probably just a minor discrepancy. However, it’s still worth checking this out further to make sure there are no problems with your system.
The first thing to note is that 2.4.62-4.el9 is not same as upstream Apache 2.4.62. It is something that was originally forked from upstream 2.4.62 but has since received modifications (usually backported patches).
Then the next step is to ask what Red Hat says about the CVE? For example:
Red Hat does not deem that CVE so severe that they would have done something about it (“Fix deferred”) yet. Maybe later. They don’t offer any mitigation (workaround) for it either.
If Red Hat does not offer a fix for RHEL 9, then it is unlikely that AlmaLinux would offer fix for AlmaLinux 9.
If a fix has been released, then changelog of package may/should mention it.
The changelog you can read. For example:
rpm -q --changelog httpd | grep -3 -i cve
Of the four CVE that you did list, none has received a fix for RHEL – two are “Fix deferred”, two “Affected” – and none has mitigation. The affected are more likely to get a patch.
You have to read the description of each CVE and determine yourself how serious they are for your servers and whether you can mitigate the risk in some way.
Unless a specific module is loaded or you are running a special configuration, I believe your environment is not affected.
That’s likely why Red Hat has also released fixed packages only for certain cases.